Energy, water & utility SCADA operators
Monitor Purdue Level 0–2 PLC registers and engineering workstation allowlists passively without disrupting deterministic control-loop timing.
Government, Critical-Infrastructure (OT/ICS/SCADA) & Enterprise Sovereign Cyber Defense OS: passive Modbus/DNP3/S7comm wire guard, OWASP Coraza WAF, Cilium Tetragon eBPF, and STIX 2.1 air-gap threat diode.
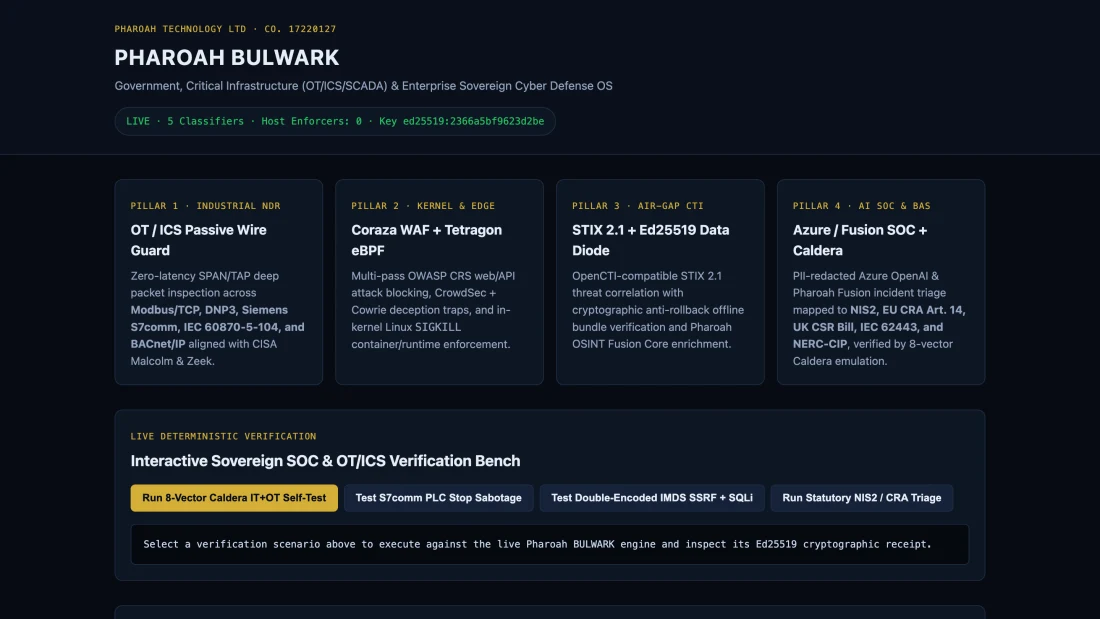
Pharoah BULWARK combines passive industrial protocol inspection (Modbus/TCP, DNP3, Siemens S7comm, IEC 60870-5-104, and BACnet/IP), OWASP Coraza WAF multi-pass attack inspection, Cilium Tetragon Linux kernel eBPF enforcement policy generation, and Ed25519-signed STIX 2.1 air-gap threat intelligence bundles.
Inspects Modbus/TCP, DNP3, Siemens S7comm, IEC 60870-5-104, and BACnet/IP telemetry against Purdue Level 0–4 zone boundaries and Safety-Instrumented System (SIS) register write locks.
Multi-pass URL/entity-decoded inspection blocking SQLi, XSS, cloud IMDS SSRF, RCE, LFI, and JNDI injection alongside MITRE ATT&CK Enterprise & ICS Sigma correlation.
Verifies OASIS STIX 2.1 threat bundles wrapped in Ed25519 + SHA-256 anti-rollback envelopes with monotonic sequence enforcement.
Every appliance service in the core Docker Compose manifest is loopback-bound (127.0.0.1) and validated in CI to contain only pinned, commercially permissive open-source images.
Monitor Purdue Level 0–2 PLC registers and engineering workstation allowlists passively without disrupting deterministic control-loop timing.
Import STIX 2.1 threat indicators across an air-gap boundary using Ed25519-signed bundles that reject replayed or rolled-back sequences.
BULWARK inspects Modbus/TCP, DNP3, Siemens S7comm, IEC 60870-5-104, and BACnet/IP telemetry, mapping unauthorized function codes and register writes directly to MITRE ATT&CK for ICS.
No. CI validation enforces that the core sovereign appliance compose stack uses only pinned Apache-2.0, MIT, and BSD-licensed images bound to 127.0.0.1.
Every Pharoah BULWARK deployment is engineered around your network topology, SPAN/TAP mirror ports, Purdue zone map, and regulatory jurisdiction.
Bespoke deployments start from £10,000 by written quotation under Pharoah Technology Ltd.
Government, Critical-Infrastructure (OT/ICS/SCADA) & Enterprise Sovereign Cyber Defense OS: passive Modbus/DNP3/S7comm wire guard, OWASP Coraza WAF, Cilium Tetragon eBPF, and STIX 2.1 air-gap threat diode.
A hardened private phone and secure router system, configured before it reaches you.
Explore →All Pharoah estate Security OS systems — including Pharoah BLACKLINE, Security Core, OCULUS, SENTRY, Agent Shield, Sovereign Recovery, SENTINEL and BULWARK — sold under the Pharoah Technology banner as bespoke systems from £10,000.
Explore →An advanced software engineering platform built around ownership, production discipline, deployment and long-term maintainability.
Explore →